Email: [email protected] Ligue agora! +55-11-3717-5537
Scalable Data Center and Carrier-Graded Security Systems
FortiGate 5000 series chassis-based security systems use highly-flexible AdvancedTCA™ (ATCA)-compliant architecture that enable the FortiGate 5000 series to protect complex, multi-tenant cloud-based security-as-a-service and infrastructure-as-a-service environments. Purpose-built by Fortinet, the FortiGate 5000 series integrates modular carrier-class hardware components with advanced FortiASIC™ acceleration and consolidated security from the FortiOS™ operating system.
Consolidated Security Solutions
FortiGate 5000 series appliances give you the ability to deploy a wide range of Fortinet’s UTM inspection capabilities, including firewall, IPS, application control, VPN, and web filtering. These features can be scaled as required by adding more security blades. Each system also supports FortiGuard® security subscription services to deliver dynamic, automated updates and ensure up-to-date protection against sophisticated threats. In addition, the devices support a web-based GUI, ‘single pane of glass’ management console, and on-board reporting.
By consolidating multiple security enforcement technologies into a single system, the FortiGate 5000 series eliminate disparate hardware devices and software solutions, greatly simplifying security gateway implementation and reducing total cost of ownership.
| Key Features & Benefits | |
|---|---|
| Unmatched Performance and Security | ASICs powered security blades with industry’s validated security OS deliver outstanding capability for massive networks. |
| Highly Scalable | Chassis system that allows organizations to add capability when needed. |
| High Speed Interfaces | Keeping pace with today’s network infrastructure and demands with high density 40 Gbps and 10 Gbps connectivity. |
Flexible and Scalable
Chassis
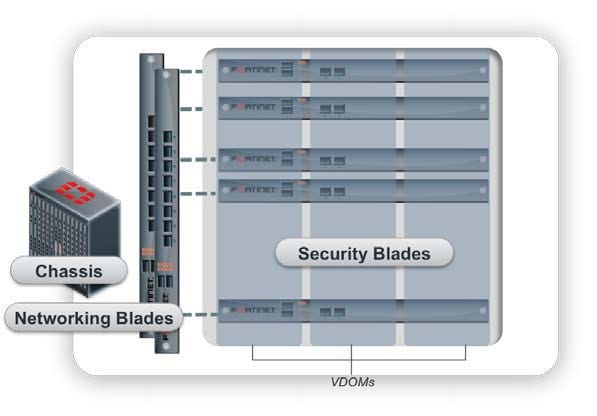
The chassis enables the flexible system to scale effortlessly and with little disruptions by allowing hot swapped blades to be added according to desired requirements. The system can also be configured for various resilience designs within the chassis as well as between chassis. The rack mount ATCA chassis provides centralized and redundant power supplies to its blades. With exception of the FortiGate 5020, the chassis may be powered by either DC or AC with additional power interface. It facilitates backplane communications between the blades which may be used for HA heartbeat and other control and data communications.
The FortiGate 5060, FortiGate 5140B and FortiGate 5144C may house shelf managers that control chassis power allocation, monitor chassis operating parameters, monitor and control chassis cooling, and can signal alerts via alarm module if the chassis encounters problems.
Security Blades
High performance, ASICs powered security blades run on FortiOS or FortiCarrier which apply access policies and security profiles on the traffic they received from the networking blades via backplane or front panel interfaces. These blades may operate in NAT/route and/or transparent mode. They also support virtual systems (VDOMs) within the cluster.
Networking Blades
Up to two networking blades may be installed on a FortiGate 5060, FortiGate 5140B and FortiGate 5144C on designated slots. These blades connect the system to the network while connected to the multiple security blades via the chassis’s backplane. The networking blade clusters the security blades with traffic distribution.
Networking blades can assign security blades into service groups which are isolated clusters coexisting in a single chassis. Two networking blades may either operate as activepassive HA or separately with its own clusters.
Next Generation Perimeter Security
Firewalls alone aren’t enough to block today’s blended threats and attacks. Data centers require multi-layered security technologies that examine entire packet flows, from content inspection through reassembly, stopping threats at the perimeter. The FortiGate 5000 series offers this critical functionality without compromising performance and scalability.
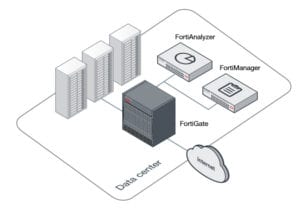
MSSP Core Security
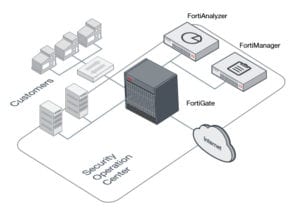
The FortiGate 5000 series delivers comprehensive security for Managed Security Service Providers (MSSPs). The full suite of ASIC-accelerated security modules allows for customizable features for specific customers, while virtualization features like Virtual Domains (VDOMs) provide up to 6,000 separate security domains. Finally, the full suite of Fortinet integrated management applications — including granular reporting features — offer unprecedented visibility into the security posture of customers while identifying their highest risks.
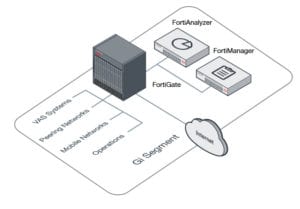
Carrier-Graded Security
The ATCA chassis and components of the FortiGate 5000 series are ideal for telecommunication operators and service providers with standard-based assurance for reliability and robustness. Its unbeatable high capacity is essential as data networks continue to grow rapidly in the near future.
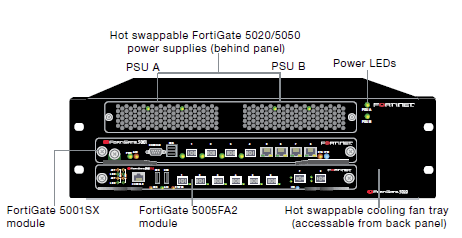
FortiGate 5020
Compact 4U chassis that contains two redundant AC power modules and can install one or two FortiGate 5000 security blades.
* Available options depending on chassis models *
* Available on 5060 and 5140B
FortiGate 5001B
Security blade ideal for basic firewalling using NP4.
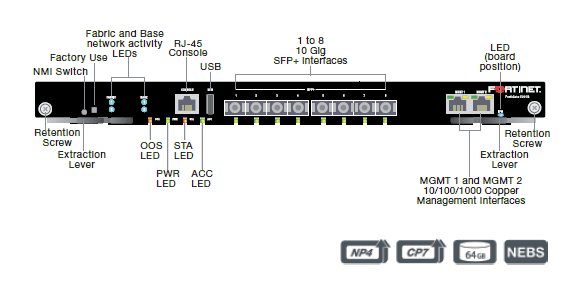
FortiGate 5001C
Security blade that is powered by CP8 and NP4 for superior firewall and UTM performance.
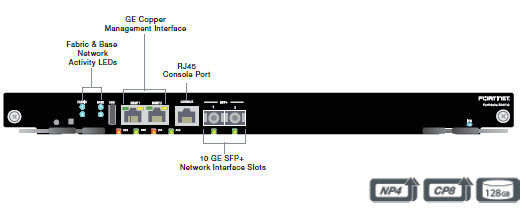
FortiGate 5101C
Powered by FortiASIC SP3 to provide unmatched UTM and IPv6 Firewall Performance, most ideal for next generation networks.
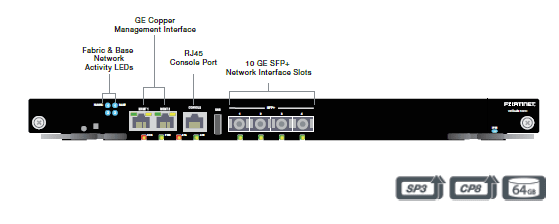
FortiGate 5001D
Latest purpose-built FortiGate security blade with carrier-class capacity and protection.
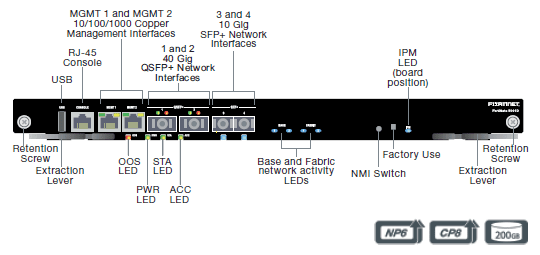
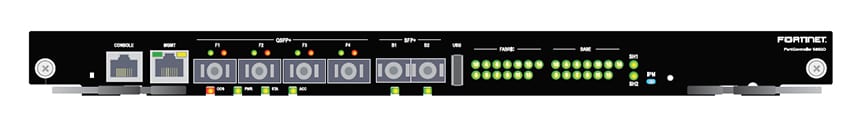
FortiController 5902D
Hybrid blade that can operate either as networking or security blade, benefits users who need to scale up UTM performance as traffic grows.
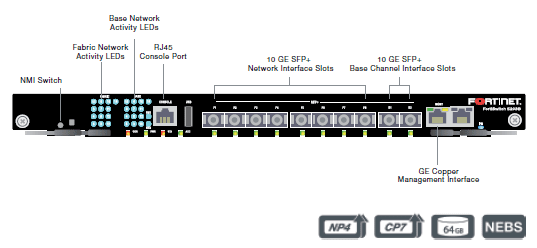
FortiSwitch 5203B
Flexible security blade that provides investment protection by transforming into a networking blade when scalability is required.
Powered by FortiASIC
Content Processor: Accelerate computationally intensive tasks
Network Processor: The heart of low latency and high performance traffic processing
FortiSwitch 5003B
Basic L2 switching blade for aggregating security blades within a chassis.
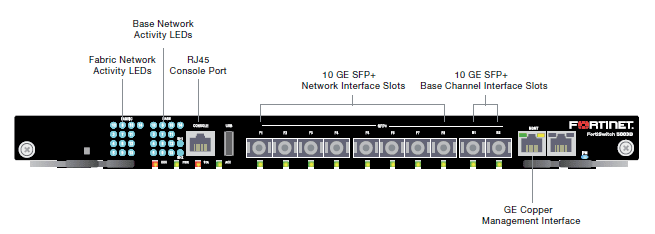
FortiSwitch 5203B
Flexible networking blade that can either operate as a standalone full featured FortiGate or in content cluster mode, as a FortiGate unit (weighted) load balancing traffic to one or more security blades.
FortiController 5103B
As a high capacity stateful load balancer, this networking blade distributes sessions to multiple FortiGate security blades using state of the art FortiASIC TP acceleration.
FortiController 5902D
Hybrid blade that can operate either as networking or security blade, benefits users who need to scale up UTM performance as traffic grows.
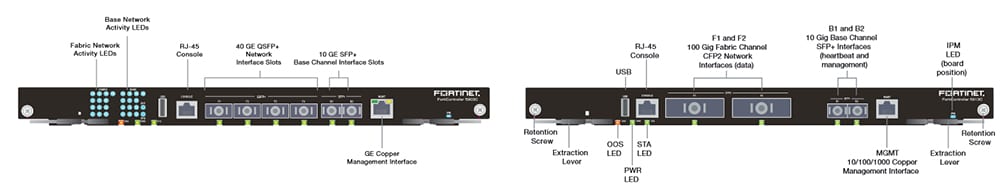
FortiController 5903C/5913C
High Performance networking blade that provides 10/40-gigabit fabric and 1-gigabit base backplane channel layer-2 switching in a dual star architecture.
FortiGate 5000-Series Clustering
The networking blades, security blades and the chassis together form clusters. This technique load balances network traffic across the cluster, helping to enhance the scalability, reliability, and availability of mission-critical IP-based services, such as firewall, antivirus, web filtering and IPS. It also provides high availability by detecting host failures and automatically redistributing traffic to the hosts within a chassis. Clustering simplifies large scale security gateway deployment as configuration synchronization and firmware upgrades can be executed automatically within the clusters.
FortiGate 5053B and PowerSupplyUnit 5000B
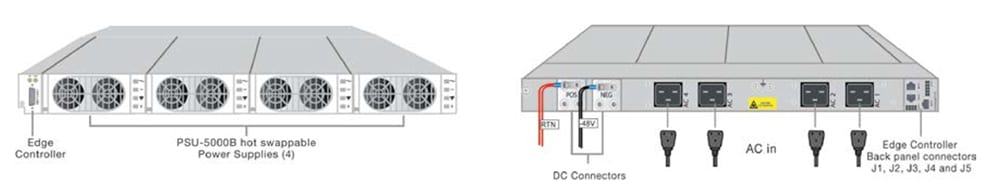
The FortiGate 5053B is a 1U 19-inch rack mount power supply shelf with PSU-5000B hot swappable power supplies to convert AC pow er to DC power and to supply power to a FortiGate 5000-series chassis.
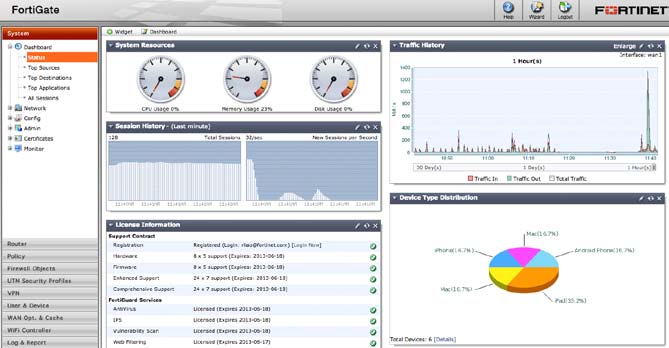
FortiOS Dashboard — Single Pane of Glass Management
Ease of Use
FortiOS lowers operation costs and reduces IT staff workloads. Physical or virtual FortiGate appliances give you the flexibility to match your security to your environment while enforcing a uniform security policy. Single pane of glass management and centralized analysis ensure consistent policy creation and enforcement while minimizing deployment and configuration challenges.
Comprehensive Systems Integration
Integration with external systems is possible with wide range of interfacing protocol support and certified solution partners. Network operators can rely on facilities such as SNMP, sFlow and syslog for monitoring purposes. Integration with provisioning systems and custom portals are also possible with Web Service APIs via FortiManager. Scripting using various scripting languages is also supported by manipulating CLI commands.
Superior IPS Capabilities
The FortiGuard IPS subscription service provides FortiGate customers with the latest defenses against stealthy network-level threats. With signatures of more than 4000 known threats, it enables FortiGate to stop attacks that evade conventional firewall defenses. It also provides behavior-based heuristics, enabling the system to recognize threats for which no signature has yet been developed.
Unique Visibility and Control
FortiOS allows greater traffic visibility and more consistent, granular control over users, devices, applications and sensitive data. Dashboard widgets allow administrators to quickly view and understand real-time network activities and threat situations.
Robust Virtual Systems
FortiOS VDOMs is a proven method of dividing a FortiGate unit/cluster into two or more virtual units that function as multiple independent units. It has the industry’s most comprehensive virtualization capabilities that meet today’s complex MSSP deployments.
Flexible Role-based Administration
Access profiles can be defined to provide granular access to VDOMs and system functionalities. This is valuable in facilitating enterprise-class or complaint security operation workflows.
Identity-Centric Enforcement
FortiOS supports both local and remote authentication services such as LDAP, RADIUS and TACACS+ to identify users and apply appropriate access policies and security profiles accordingly. It may also simplify identity-based implementations and also provide seamless users authorization experience with various single sign-on capabilities. One such application is to retrieve subscriber’s information via RADIUS accounting messages and apply appropriate security services dynamically for a managed service provider. FortiOS has strong PKI and certificate-based authentication services and also integrates an internal two-factor token server for additional security.
Proven with Industry Validation
FortiGate received the most industry’s certifications among its competitions, assuring top-notch feature quality to provide you with air tight security and best-of-breed security protection.
Powerful Policy Management
It is common in service provider and data center networks to have hundreds, if not thousands of security policies, hence to be able to manage these policies effectively is critical to minimize configuration errors and complexity. FortiOS has the unique ability to provide two forms of policy management views — Global and Section view helps administrators to choose an option that they are most familiar with or suit their requirements best. It also provides powerful features such as policy object search, tagging, sorting and filtering. Policy objects can easily be edited from the policy table. With FortiManager integration, customers may also have the ability to setup sophisticated policy implementation and provisioning workflows for compliance or operation requirements. Detailed configuration audit trail is supported and can reside externally for secured storage with FortiAnalyzer.
Extensive Network Support
FortiOS supports numerous network design requirements and interops with other networking devices. This includes support for a wealth of routing, multicasting and network resiliency protocols. Administrators can also configure interfaces for VLANs, VLAN trunks, port aggregation and one-arm sniffer mode.
Broad IPv6 Support
Maintaining security for both IPv4 and IPv6 traffic will be crucial to the success of mixed networks. Malware and network threats are independent of IPv4 or IPv6. FortiOS is able to use IPv6 security policies to provide access control and FortiGuard Unified Threat Protection (UTP) for IPv6 traffic. FortiOS has been successfully evaluated as compliant with core protocol and interoperability tests defined by IPv6 Ready Logo Phase 2.
More Features with FortiCarrier Software License
| FortiGate 5020 | FortiGate 5060 | FortiGate 5140B | FortiGate 5144C | |
|---|---|---|---|---|
| Hardware Specifications | ||||
| Available Slots | 2 | 6 | 14 | 14 |
| High Availability Backplane Fabric | Built-in | Built-in | Built-in | Built-in |
| 40 Gbps Backplane Support | – | – | – | Yes |
| Shelf Manager (Default / Maximum) | – | 1 / 2 | 1 / 2 | 1 / 2 |
| Dual Networking Blade Support | No | Yes | Yes | Yes |
| Dimensions | ||||
| Height x Width x Length (inches) | 5.25 x 17 x 15.5 | 8.86 x 17.64 x 18.82 | 22.63 x 19 x 22.6 | 24.44 x 19.06 x 21.63 |
| Height x Width x Length (cm) | 13.3 x 43.2 x 39.4 | 22 x 44.8 x 47.8 | 57.5 x 48.3 x 57.4 | 62.1 x 48.4 x 55.0 |
| Weight | 35.5 lb (16.1 kg) | 38 (17.3 kg) | 84 lb (38 kg) | 108 lb (50 kg) |
| Maximum Capacity** | ||||
| Firewall Throughput | 160 Gbps | 480 Gbps | 1.12 Tbps | 1.12 Tbps |
| Power and Environment | ||||
| Power Required | AC | DC/AC1 | DC/AC1 | DC/AC1 |
| Chassis Only Power Consumption (Maximum) *** | – | 350 W | 530 W | 960 W |
| Heat Dissipation (Maximum) *** | – | 1194 BTU/h | 1808 BTU/h | 3,276 BTU/h |
| Operating Temperature | 32–104°F (0–40°C) | 41–104°F (5–40°C) | 32–104°F (0–40°C) | 32–104°F (0–40°C) |
| Storage Temperature | -13–158°F (-35–70°C) | 23–131°F (-5–55°C) | -13–158°F (-35–70°C) | -13–158°F (-35–70°C) |
| Humidity | 5–90% non-condensing | 5–85% non-condensing | 5–90% non-condensing | 5–90% non-condensing |
| Compliance | ||||
| Certifications | FCC Part 15 Class A, C-Tick, VCCI, CE, BSMI, UL/cUL | |||
1 Optional FortiGate 5053B Power Supply Shelf used to provide AC power to the FortiGate
** Based on fully populated FortiGate 5001D
*** Please refer to respective Chassis Guide for computation of total power requirement.
| FortiGate 5001B | FortiGate 5001C | FortiGate 5101C | FortiGate 5001D | FortiSwitch 5203B* | FortiController 5902D* | |
|---|---|---|---|---|---|---|
| Interfaces and Storage | ||||||
| 40 GE QSFP+ Ports | – | – | – | 2 | – | 4 |
| 10 GE SFP+ Ports | 8 | 2 | 4 | 2 | 10 | 2 |
| GE RJ45 Ports | 2 | 2 | 2 | 2 | 1 | 1 |
| RJ45 Console Port | 1 | 1 | 1 | 1 | 1 | 1 |
| Included Transceivers | 2x 10 GE SFP+ SR | 2x 10 GE SFP+ SR | 2x 10 GE SFP+ SR | 2x 10 GE SFP+ SR | 2x 10 GE SFP+ SR | 2x 10 GE SFP+ SR |
| Local Storage | 64 GB | 128 GB | 64 GB | 200 GB | 64 GB | 128 GB |
| Syetem Performance | ||||||
| Firewall Throughput (1518 / 512 / 64 byte UDP packets) | 40 / 40 / 40 Gbps | 40 / 40 / 40 Gbps | 40 / 40 / 10 Gbps | 80 / 80 / 45 Gbps | 40 / 40 / 40 Gbps | 80 / 80 / 50 Gbps |
| Firewall Latency (64 byte UDP packets) | 4 μs | 4 μs | 7 μs | 3 μs | 4 μs | 3 μs |
| Firewall Throughput (Packets Per Second) | 60 Mpps | 60 Mpps | 15 Mpps | 67.5 Mbpps | 60 Mpps | 75 Mpps |
| Concurrent Sessions (TCP) | 20 Mil | 29.5 Mil | 10 Mil | 23 Mil | 20 Mil | 50 Million |
| New Sessions/Sec (TCP) | 170,000 | 210,000 | 235,000 | 565,000 | 170,000 | 155,000 |
| Maximum Firewall Policies | 100,000 | 100,000 | 100,000 | 100,000 | 100,000 | 100,000 |
| IPsec VPN Throughput (512 byte packets) | 17 Gbps | 17 Gbps | 22 Gbps | 25 Gbps | 17 Gbps | 15 Gbps |
| Gateway-to-Gateway IPsec VPN Tunnels | 40,000 | 40,000 | 40,000 | 40,000 | 40,000 | 40,000 |
| Client-to-Gateway IPsec VPN Tunnels | 64,000 | 64,000 | 64,000 | 64,000 | 64,000 | 64,000 |
| SSL-VPN Throughput | 1.3 Gbps | 3.6 Gbps | 1.3 Gbps | 6.5 Gbps | 1.3 Gbps | 6.5 Gbps |
| Concurrent SSL-VPN Users (Recommended Maximum) | 20,000 | 20,000 | 25,000 | 25,000 | 20,000 | 25,000 |
| IPS Throughput | 7.8 Gbps | 12 Gbps | 9.4 Gbps | 18 Gbps | 7.8 Gbps | 18 Gbps |
| Antivirus Throughput (Proxy Based / Flow Based) | 2 / 2.5 Gbps | 3 / 4 Gbps | 2 / 5 Gbps | 5.6 / 13 Gbps | 2 / 2.5 Gbps | 3.8 Gbps |
| Virtual Domains (Default / Maximum) | 10 / 500 | 10 / 500 | 10 / 500 | 10 / 500 | 10 / 500 | 10 / 500 |
| Maximum Number of FortiTokens | 5,000 | 5,000 | 5,000 | 5,000 | 5,000 | 5,000 |
| Maximum Number of Registered FortiClients | 20,000 | 20,000 | 20,000 | 20,000 | 20,000 | 20,000 |
| Maximum Number of FortiAPs | 1,024 | 1,024 | 1,024 | 1,024 | 1,024 | 1,024 |
| Power and Environment | ||||||
| Power Consumption (Average / Maximum) | 194 / 233 W | 187 / 225 W | 197 / 236 W | 189 / 226 W | 210 / 250W | 223 / 270 W |
| Heat Dissipation (Average) | 795 BTU/h | 768 BTU/h | 805 BTU/h | 774 BTU/h | 853 BTU/h | 919 BTU/h |
| Operating Temperature | 32–104°F (0–40°C) | 32–104°F (0–40°C) | 32–104°F (0–40°C) | 32–104°F (0–40°C) | 32–104°F (0–40°C) | 32–104°F (0–40°C) |
| Storage Temperature | -13–158°F (-25–70°C) | -13–158°F (-25–70 °C) | -13–158°F (-25–70°C) | -13–158°F (-25–70°C) | -13–158°F (-25–70°C) | -13–158°F (-25–70°C) |
| Humidity | 20–90% non-condensing | 20–90% non-condensing | 20–90% non-condensing | 20–90% non-condensing | 20–90% non-condensing | 20–90% non-condensing |
| Compliance | ||||||
| Certifications | FCC Part 15 Class A, C-Tick, VCCI, CE, UL/cUL, CB, ICSA Labs: Firewall, IPsec, IPS, Antivirus, SSL-VPN | |||||
| NEBS Certified | Yes | – | – | – | Yes | Yes |
* Operating in Standalone Mode
Note: All performance values are “up to” and vary depending on system configuration. Antivirus performance is measured using 44 Kbyte HTTP files. IPS performance is measured using 1 Mbyte HTTP files.
| FortiSwitch 5003B | FortiSwitch 5203B* | FortiController 5103B | FortiController 5902D* | FortiController 5903C | FortiController 5913C | ||
|---|---|---|---|---|---|---|---|
| Interfaces | |||||||
| Fabric Channel Interfaces | 8x 10 GE SFP+ | 8x 10 GE SFP+ | 8x 10 GE SFP+ | 4x 40 GE QSFP+ | 4x 40 GE QSFP+ | 2x 100 GE CFP2 | |
| Base Channel Interfaces | 2x 10 GE SFP+ | 2x 10 GE SFP+ | 2x 10 GE SFP+ | 2x 10 GE SFP+ | 2x 10 GE SFP+ | 2x 10 GE SFP+ | |
| Management Interfaces | 1x GE RJ45 | 1x GE RJ45 | 1x GE RJ45 | 1x GE RJ45 | 1x GE RJ45 | 1x GE RJ45 | |
| Included Transceivers | 2x 10 GE SFP+ SR | 2x 10 GE SFP+ SR | 2x 10 GE SFP+ SR | 2x 10 GE SFP+ SR | 2x 10 GE SFP+ SR | 2x 10 GE SFP+ SR | |
| 40 GE Backplane Fabric Support | – | – | – | Yes | Yes | Yes | |
| 10 GE Backplane Fabric Support | Yes | Yes | Yes | Yes | Yes | Yes | |
| GE Backplane Fabric Support | Yes | Yes | Yes | – | – | – | |
| System Performance | |||||||
| Maximum Traffic Throughput | 80 Gbps | 40 Gbps | 60 Gbps | 80 Gbps | 120 Gbps | 200 Gbps | |
| Maximum Concurrent Sessions | – | 20 Million | 110 Million | 50 Million | 135 Million | 135 Million | |
| New Sessions/Second (TCP) | – | 170,000 | 1.26 Million | 155,000 | 3.2 Million | 3.6 Million | |
| Power and Environment | |||||||
| Power Consumption (Average / Maximum) | 150 / 180 W | 210 / 250 W | 213 / 255 W | 223 / 270 W | 250 / 400 W | 280 / 400 W | |
| Heat Dissipation | 614 BTU/h | 853 BTU/h | 754 BTU/h | 919 BTU/h | 1360 BTU/h | 955 BTU/h | |
| Operating Temperature | 32–104°F (0–40°C) | 32–104°F (0–40°C) | 32–104°F (0–40°C) | 32–104°F (0–40°C) | 32–104°F (0–40°C) | 32–104°F (0–40°C) | |
| Storage Temperature | -13–158°F (-35–70°C) | -13–158°F (-35–70°C) | -13–158°F (-35–70°C) | -13–158°F (-35–70°C) | -13–158°F (-35–70°C) | -13–158°F (-35–70°C) | |
| Humidity | 20–90% non-condensing | 20–90% non-condensing | 20–90% non-condensing | 20–90% non-condensing | 20–90% non-condensing | 5–90% non-condensing | |
| Compliance | |||||||
| Certifications | FCC Part 15 Class A, C-Tick, VCCI, CE, UL/cUL, CB | ||||||
FortiGate Chassis Platforms Clustering The networking blades, security blades and the chassis together form clusters. This technique load balances network traffic across the cluster, helping to enhance the scalability, reliability, and availability of mission-critical IP-based services, such as firewall, antivirus, web filtering, IPS, and so on. It also provides high availability by detecting host failures and automatically redistributing traffic to the hosts within a chassis. Clustering simplifies large scale security gateway deployment as configuration synchronization and firmware upgrades can be executed automatically within the clusters.
| Content Clustering (CC) | Session-aware load Balancing Clustering | |
|---|---|---|
| Clustering Features | ||
| Technology | Modified FortiOS Active-Active HA cluster with Chassis | Intelligent Network load balancing within Chassis |
| Ideal Use Case | Scaling UTM performance for MSSP | High performance CGN and Internet security gateway for Service Provider |
| Configuration Synchronization and Firmware Upgrades | Yes | Yes |
| Session Termination (eg, VPN, Explicit Proxy) | Yes | Yes. On Primary Security Blade |
| Multi-segmentation | Yes | Limited |
| High Availability Setup | Intra Chassis | Inter & Intra Chassis |
| Networking Blades | ||
| Supported Networking Blades | FSW-5203B | FCTL-5103B |
| Security Blades | ||
| Supported Security Blades | FG-5001B, FG-5001C, FG-5101C, FG-5001D | FG-5001B, FG-5001C, FG-5101C, FG-5001D |
FortiGate 5053B and PowerSupplyUnit 5000B The FortiGate 5053B is a 1U 19-inch rack mount power supply shelf with PSU-5000B hot swappable power supplies to convert AC power to DC power and to supply power to a FortiGate 5000 series chassis.
| Non-redundant | Redundant | ||||||
|---|---|---|---|---|---|---|---|
| Number of PSUs | 1 | 2 | 3 | 4 | 1+1 | 2+1 | 3+1 |
| 5053B with PSU-5000B (185–307V AC High Line Input) | 2,725 W | 5,450 W | 8,175 W | 10,900 W | 2,725 W | 5,450 W | 8,175 W |
| 5053B with PSU-5000B (100–184V AC Low Line Input, North America, Mexico, Japan, etc.) | 1,200 W | 2,400 W | 3,600 W | 4,800 W | 1,200 W | 2,400 W | 3,600 W |
Download the Fortinet FortiGate-5000 Series Datasheet (.PDF)
| Licença | Monthly Firewall Management, Monitoring, and Support | |
|---|---|
| 1 ano – Monthly Firewall Management, Monitoring, and Support, 12 months | #MNG-FW-LG |
| 1 ano – Monthly Firewall Management, Monitoring, and Support, 36 Months | #MNG-FW-LG36 |
Clique aqui e responda nosso questionário!
Precisa comprar, renovar licença, instalar ou migrar seu equipamento ?
Planejamos sua aquisição, instalação, implantação ou migração, para mais informações faça contato com a TND Brasil através do telefone (11) 3717-5537 , e-mail [email protected] ou envie uma mensagem.